Threat Detection
Detect malicious activity by inspecting sensory and log data from security controls, sophisticated security systems, and threat intelligence.
Complete Security Against Malicious Actors 24/7,
365 Days a Year to Safeguard the Most Valuable Assets
Security is a major challenge for businesses globally as cyber threats evolve and become more complex. The GLS Security Operations Center (SOC) was specifically designed to provide organizations with comprehensive security at scale with our tailored solutions to solve any complex challenge through an in-depth defense strategy. As an OEM agnostic provider, we can seamlessly integrate your existing security technology tools and investments into our SOC operations to maximize their value and address any vulnerabilities.
Access 24/7/365 monitoring, detection, response, and remediation services that help reduce risk, accelerate recovery, and strengthen operational resilience
GLS delivers 24/7/365 monitoring, streamlined network deployment, broadband management, and flexible carrier support for reliable business connectivity.
We use infrastructure telemetry and continuous monitoring to detect threats, contain incidents, and quickly restore affected systems for strong security.
Unified visibility into network performance and security events, helping analysts correlate threats in real time.
Shared tooling and workflows help GLS teams identify, contain, and act on threats faster, reducing handoffs and delays.
GLS cuts duplicate tools, staffing, and overhead by streamlining vendors and licensing across both disciplines.
Our converged team connects network, log, and endpoint data to clarify what happened, how it spread, and what to fix.
GLS closes gaps between siloed teams with integrated on-call workflows, ensuring every alert gets addressed.
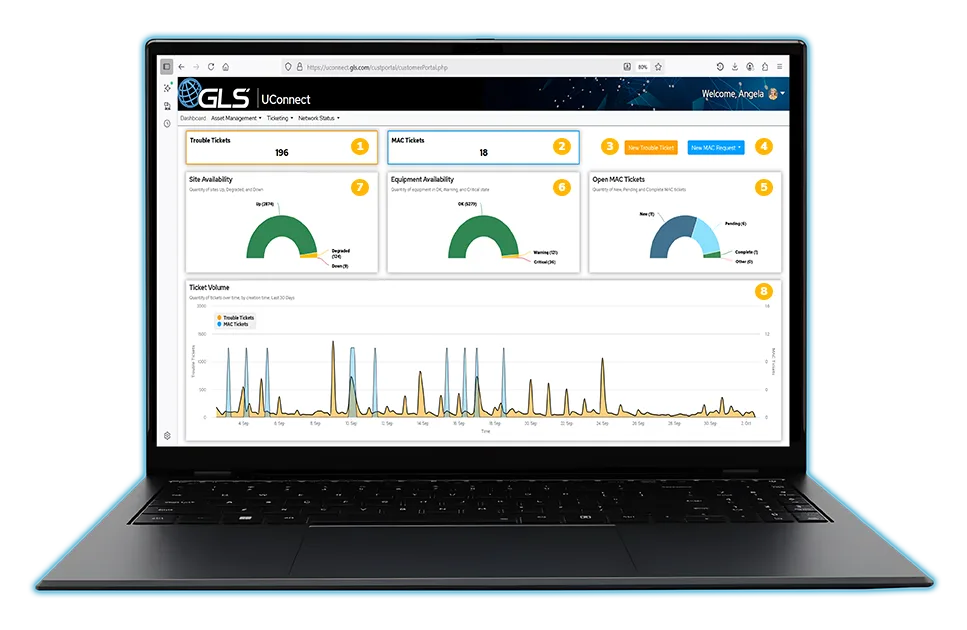
GLS's proprietary UConnect Portal provides a comprehensive dashboard for NOC services, giving users a single site to review analytics, manage devices, submit trouble tickets, and access essential network management resources.
Prevention allows GLS to deploy & manage security controls to find and fix problems within a business's organization.
Detect malicious activity by inspecting sensory and log data from security controls, sophisticated security systems, and threat intelligence.
Integrate data from client assessment tools utilized to comply with regulatory milestones and become continuously compliant.
Identify, categorize, and discover all network and service assets requiring protection and monitoring.
Manage, co-manage, + monitor all controls, logs, and data to detect and respond to anomalies and malicious activity.
Monitor human activity and detect suspicious or unusual behaviors based on client-specific playbooks.
Use APIs and agents to aggregate data from all assets requiring security monitoring into a managed and tuned SIEM.
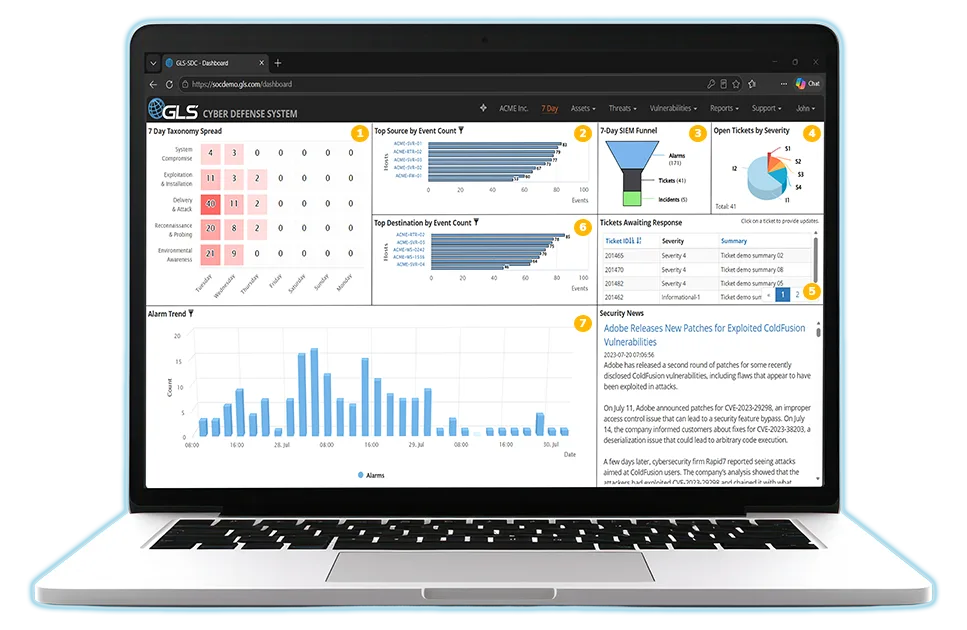
Organizations depend on complex technologies that do not always work efficiently together. As part of our SOC solutions, GLS's proprietary Cyber Defense System provides a centralized portal that helps unify security operations, improve visibility, and enable seamless performance across the environment.
| Additional services available | |
|---|---|
| Host Intrusion Detection (HIDS) | PCI Support |
| HIDS Software Application Agent: Monitors servers for suspicious activity across system logs, applications, kernel processes, network resources, and critical files to help detect and respond to threats quickly. | Simplified PCI Compliance: Streamline compliance efforts with integrated tools for SAQ management, scanning, documentation, policy support, and compliance reporting. |
| Application Control: Restricts software execution to authorized applications using customer-defined allowlists, helping prevent unauthorized code and unknown threats. | Proactive Security Validation: Identify vulnerabilities before they become risks through recurring external and internal security assessments. |
| Change Control With File Integrity Monitoring: Provides near real-time visibility into file, registry, and account changes while helping prevent unauthorized modifications and tampering. | Layered Protection for Critical Systems: Secure payment environments with network segmentation, encryption, strong access controls, and comprehensive monitoring. |
| Governance & Audit Readiness: Maintain compliance with detailed audit trails, log retention standards, user activity tracking, and configuration change reporting. | |